Cybersecurity Strategies for Small Businesses With Remote Teams
Posted on
Product Design
Posted at

It is 9:40 on a Tuesday morning. A bookkeeper for an 18-person consultancy opens her personal laptop at a coworking space, joins the guest Wi-Fi, and signs into the company's Microsoft 365 tenant. She approves a push notification on her phone without really reading it, because she gets three or four of those a week. By 10:15 someone else is reading her mailbox from a residential IP address two countries away, has created a hidden inbox rule that files anything containing the word "invoice" into an archive folder, and is quietly waiting for the next supplier payment cycle.
Nothing in that sequence involved a firewall, a server room, or an office network. No malware ran. No vulnerability was exploited. The entire event happened across an identity, a device, and a cloud application, which is exactly where most small-business work now lives.
This is the practical problem that remote and hybrid work created. The security controls most small businesses inherited were designed around a place: one office, one network, one internet connection, one set of company-owned machines sitting behind one firewall. Those assumptions no longer describe how a distributed team works. Today the path from employee to company data usually runs through a home network, a laptop, a phone, a browser, a handful of SaaS platforms, several third-party integrations, and occasionally a contractor in another time zone.
The modern small-business security perimeter follows the employee, the identity, the device, the application, and the data. It does not follow the office.
That shift is not a reason to panic, and it is not a reason to spend money you do not have. Small businesses with remote teams can reach a genuinely defensible position with a short list of controls, applied consistently, and a small number of habits practiced often enough to become normal. What they cannot do is buy a product and assume the problem is handled.
This guide explains how remote work changes your threat model, where small businesses are actually exposed, which controls deliver the most risk reduction per dollar, how to roll them out on a realistic budget, and how to build the kind of security culture that survives staff turnover and busy quarters. It includes policy frameworks you can adapt, comparison tables, a 30-60-90 day plan, incident playbooks, and detailed answers to the questions small-business owners ask most.
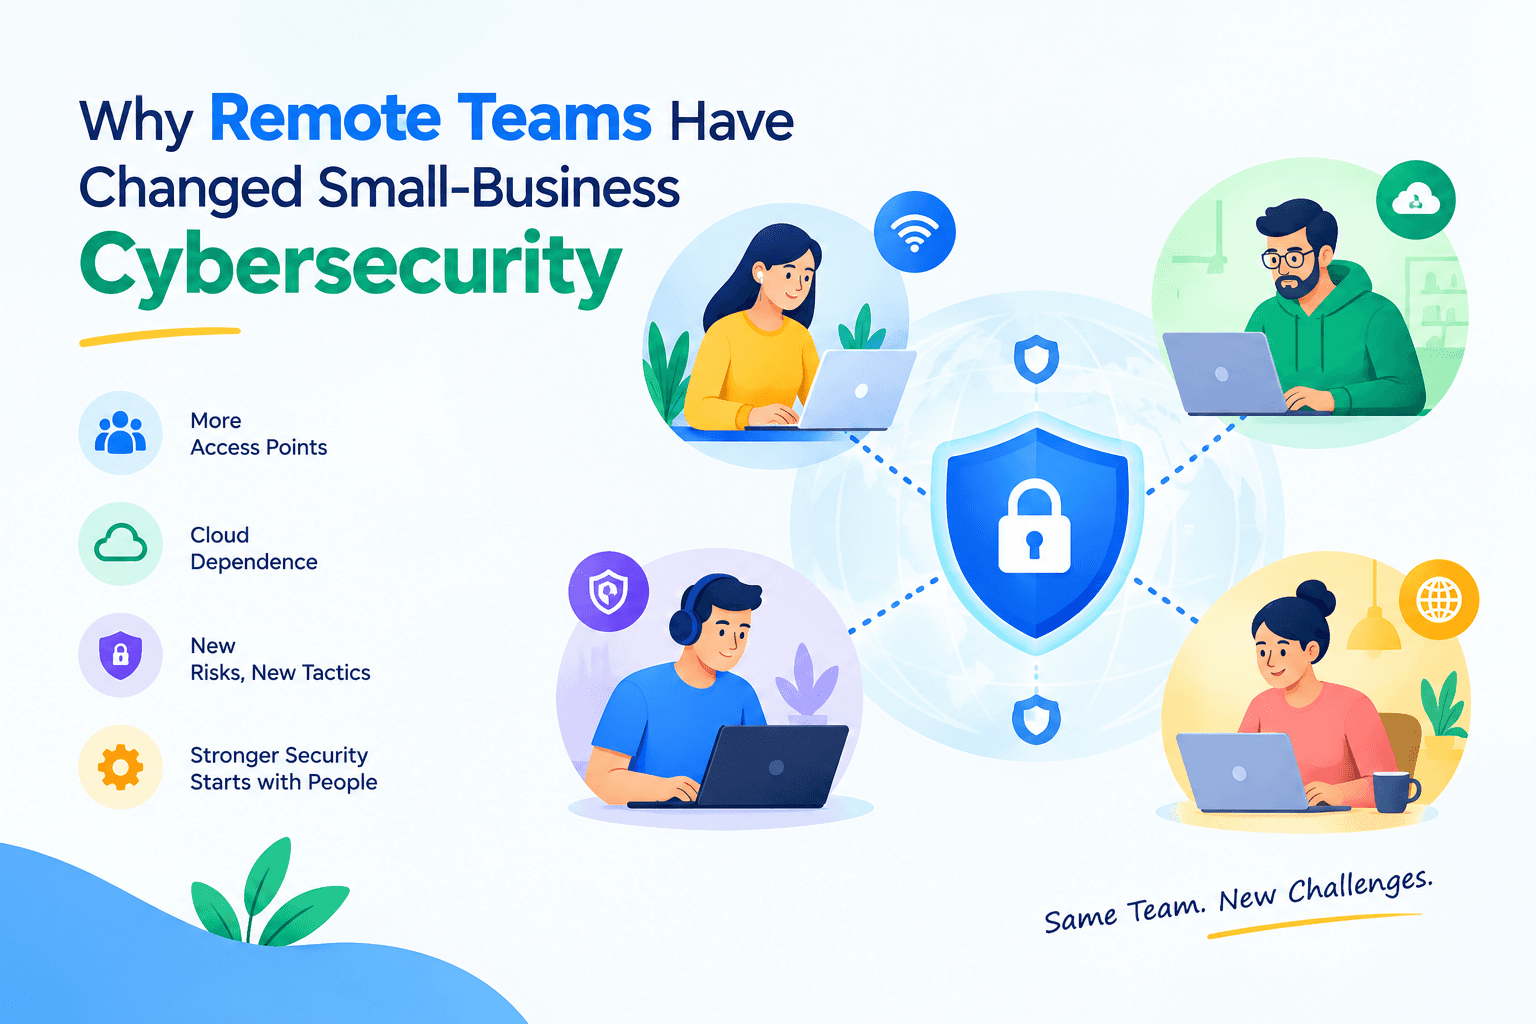
Why Remote Teams Have Changed Small-Business Cybersecurity
The traditional small-business security model was implicitly a trust model based on location. If you were in the office, plugged into the office network, on an office computer, you were treated as trusted. Everything else was outside. That model was never perfect, but it was coherent, and it let a small company buy one firewall and one antivirus subscription and feel reasonably covered.
Remote work dismantles the assumption underneath it. Consider what a distributed team actually introduces:
Distributed employees. Work happens from homes, cafés, family visits, hotels, and coworking spaces. There is no shared network to monitor and no single egress point where traffic can be inspected.
Home Wi-Fi networks. Employees connect through consumer routers that the business does not own, cannot patch, and should not attempt to manage. Those networks are shared with smart TVs, game consoles, children's tablets, and whatever IoT device was cheapest on sale.
Personal devices. Even in companies that issue laptops, personal phones almost always end up holding company email, chat, and authentication apps. The boundary between personal and corporate computing is blurry by default.
Cloud applications and SaaS dependency. Email, files, CRM, accounting, payroll, support tickets, design, code, and project management all live with vendors. Your data is reachable from any internet connection in the world by anyone who can prove they are your employee.
Remote access to legacy systems. Businesses that still run an on-premises application or a file server often expose it through remote desktop, a VPN appliance, or a port forward. These become high-value targets precisely because they offer direct, interactive access.
Mobile work. Phones authenticate, approve, receive one-time codes, hold documents, and get left in taxis.
Shared documents and links. Collaboration depends on sharing, and sharing defaults are frequently more permissive than anyone intends. "Anyone with the link" is a security decision made in half a second.
Third-party applications and OAuth integrations. A scheduling tool, an AI note-taker, or a marketing plugin can request standing access to mailboxes, calendars, and drives. That access persists long after anyone remembers approving it.
Multiple identity providers. Some staff sign in with Google, others with Microsoft, some tools have their own local accounts, and a few people use a personal account for a business system because it was quicker at the time.
Employee turnover. In a distributed company, offboarding is an administrative act rather than a physical one. Nobody collects a badge or watches someone pack a desk. Accounts stay live unless someone deliberately disables them.
Geographically distributed teams. Time zones mean fewer overlapping hours, fewer chances to confirm an unusual request face to face, and legitimate logins from many countries, which makes anomalous logins harder to spot.
Contractors and freelancers. Agencies, developers, bookkeepers, and virtual assistants are often granted access quickly, with broad permissions, on equipment the business has never seen.
The cumulative effect is that perimeter-oriented controls still matter but no longer carry the weight. A firewall protecting an office that three people visit twice a week is not a meaningful control for a company whose data lives in six SaaS platforms. Verizon's 2026 Data Breach Investigations Report, which analyzed more than 22,000 confirmed breaches, found that a third party was involved in roughly 48% of breaches, a substantial increase year over year, with attackers routinely working through vendors, cloud platforms, contractors, and application integrations rather than attacking the target directly. That is a distributed-trust problem, not a network-boundary problem.
The practical conclusion is not that offices are unsafe. It is that the controls which produce the most protection for a remote small business are the ones attached to people and data rather than to buildings: who can authenticate, from what device, into which application, with what level of privilege, and what happens when something goes wrong.
Why Small Businesses Are Attractive Cybersecurity Targets
The common framing is that criminals target small businesses because they are easy. That is too simple and it leads to the wrong conclusions. A more accurate picture has several parts.
Most attacks are opportunistic, not personal. Credential-stuffing, phishing, and mass exploitation of internet-facing software are industrial processes. They scan and spray. Whether you are a five-person studio or a five-thousand-person firm is largely irrelevant at the point of initial contact. You are selected after you respond, not before.
Small businesses hold genuinely valuable data. Customer contact lists, payment details, bank credentials, health or legal records, supplier relationships, contracts, source code, and design files all have resale or extortion value. A 12-person medical billing company handles more regulated data per employee than most large manufacturers.
Cash movement is often less supervised. A company where one person can initiate a payment and a second approves it casually over chat is a better business-email-compromise target than one with formal treasury controls. The FBI's Internet Crime Complaint Center recorded just over $3 billion in reported BEC losses in the United States in 2025 alone, from fewer than 25,000 complaints, which tells you how large the average incident is.
Credentials are the product. Stolen business logins are resold. An account in your Microsoft 365 tenant is worth money to someone who will use it to phish your customers from a legitimate domain.
You are somebody's supply chain. If you provide services, software, bookkeeping, or IT to larger organizations, your access to their systems is the actual prize. This is why enterprise customers increasingly send security questionnaires to vendors with twelve employees.
Vendor and administrative access accumulates. Small teams grant admin rights liberally because it removes friction. Those standing privileges are exactly what an attacker needs to move from a foothold to full control.
Recovery capability is usually thin. Larger organizations absorb an incident. Sophos's State of Ransomware 2026, based on a survey of more than 2,100 organizations that experienced ransomware in the prior year, found that companies with 100 to 250 employees stopped attacks before encryption or extortion only about a third of the time, while much larger organizations did so noticeably more often. The gap reflects staffing, monitoring, and rehearsed response, not luck.
The point that matters most: business size determines neither the likelihood of contact nor the severity of the consequences. A small company can lose the same customer database, face the same regulatory notification duties, and suffer proportionally worse financial damage than a large one, because a week of downtime is a much larger share of its annual revenue.
The Biggest Cybersecurity Risks for Remote Small Businesses
The risks below are ordered roughly by how often they cause real damage to small distributed teams, not by how dramatic they sound.
Phishing and Social Engineering
Phishing remains the most reliable way into a small business because it targets judgment rather than technology. For remote teams the risk is amplified by a simple structural fact: there is no one to turn to. An employee in an office can lean over and ask a colleague whether the CEO really requested a bank-detail change. An employee alone at home has to decide by themselves, often quickly, on a phone screen.
The main forms you will encounter:
Credential phishing. A convincing copy of a Microsoft, Google, or SaaS login page, delivered by email, chat, or SMS. Modern kits proxy the real login in real time, which means they capture the password, the one-time code, and the session cookie, defeating app-based MFA.
Spear phishing. Personalized messages built from LinkedIn, your website, and press releases. "Following up on the Henderson proposal" is far more effective than "Dear customer."
Business email compromise. No links, no attachments, no malware. Just a plausible email asking for a payment, a payroll change, or a gift-card purchase. There is nothing for a filter to detect.
Fake invoices and supplier fraud. A genuine-looking invoice from a supplier you actually use, with altered bank details, sent at a plausible time in the billing cycle.
Executive impersonation. A message from a spoofed or lookalike domain, frequently arriving outside business hours to discourage verification, and frequently framed as confidential.
Messaging-app scams. WhatsApp, Telegram, Teams, and Slack are increasingly used because staff apply less scrutiny to chat than to email, and because guest access or unmanaged personal accounts are common.
AI-assisted phishing. Generative tools have removed the grammatical tells people were trained to look for, and enable convincing voice or video impersonation. The FBI's 2025 report tracked AI-linked fraud as a distinct category for the first time, associating roughly $893 million in losses with it, and noted this likely understates reality because victims frequently cannot tell that AI was involved.
The defensive lesson is that awareness training alone is not enough. You need controls that make a successful phish less useful: phishing-resistant authentication, payment verification procedures that do not depend on email, and alerting on the activity that follows a compromise.
Stolen or Compromised Credentials
A password is a secret that has to be remembered, typed, stored, and transmitted. Every one of those steps leaks.
Password reuse means a breach at an unrelated consumer service becomes a breach at your company. Identity-exposure research published by SpyCloud in 2026 found billions of credential pairs circulating in criminal markets, with roughly four in ten corporate users having reused an exposed password.
Credential stuffing automates the reuse problem at scale against login pages that lack rate limiting or MFA.
Infostealer malware is the quiet, underrated threat. It runs on a personal or unmanaged device, harvests every password saved in the browser plus active session cookies, and exits. Because session cookies bypass login entirely, the attacker does not need the password or the second factor.
Shared accounts destroy attribution. When five people use one login, you cannot tell who did what, you cannot revoke access for one person, and the password is almost certainly in a chat thread somewhere.
Weak authentication on secondary systems, where MFA was never enabled because the tool "isn't important," provides the initial foothold surprisingly often.
Identity security is the load-bearing wall of remote-work security. If an attacker holds a valid identity with broad permissions, most of your other controls become decorative.
Unsecured Home Networks
Home networks deserve attention but also perspective. Modern work is overwhelmingly encrypted in transit, so the classic "attacker on the same Wi-Fi reads your traffic" scenario is much rarer than it used to be. The genuine risks are narrower:
Routers with default administrator credentials that anyone can look up
Firmware that has not been updated in years, or hardware past end of support
Weak or shared Wi-Fi passwords, sometimes handed out to visitors and neighbors
Open or captive-portal public Wi-Fi, where DNS manipulation and hostile portals are plausible
Compromised devices on the same network scanning for anything exposed
What a business can realistically require is modest and worth stating clearly in policy: use WPA2 or WPA3, change the router's admin password, keep firmware current, and do not connect work devices to networks you have no reason to trust. What a business should not attempt is managing employees' home networks. You will not succeed, it creates a privacy problem, and the effort is better spent on the device and the identity, which you can actually control.
Unmanaged Devices
An unmanaged device is one you cannot see, cannot verify, and cannot remediate. Personal laptops running an unsupported operating system, without disk encryption, with a dozen browser extensions of unknown provenance and a local folder of exported customer spreadsheets, are a common and underestimated exposure.
The core issues are:
Operating systems past end of support, which stop receiving security patches entirely
Missing patches on browsers, PDF readers, and productivity software
Unmanaged browser extensions with permission to read page content, including everything in your CRM
Unauthorized applications, including pirated software, which is a well-worn malware delivery route
Local storage of business data with no encryption and no backup
No ability to wipe or revoke if the device is lost or the employee departs
Choosing between company-owned and BYOD is one of the more consequential decisions a remote small business makes.
Factor | BYOD (employee-owned) | Company-owned |
|---|---|---|
Upfront cost | Minimal | Roughly $900–$2,000 per person, refreshed every 3–4 years |
Ongoing management | Harder; limited enforcement | Straightforward with a management platform |
Visibility into patch level | Poor unless agents are accepted | Full |
Ability to enforce encryption, screen lock, EDR | Limited and often contested | Yes |
Remote wipe | Usually restricted to a work profile at best | Full device wipe possible |
Employee privacy | Significant concerns; personal data is on the device | Clear separation |
Offboarding | Messy; data may remain | Device returned or wiped |
Best suited to | Contractors, very early-stage companies, non-sensitive roles | Anyone handling regulated, financial, or customer data; any company with compliance obligations |
A sensible middle path for growing companies is tiered: company-owned laptops for anyone touching sensitive systems, and for everyone else a conditional-access rule requiring that personal devices meet a minimum bar (supported OS, encryption on, screen lock, current patches) before they can reach company data. This gives you enforcement without demanding control of someone's private computer.
Cloud and SaaS Account Exposure
Moving to the cloud transfers responsibility for infrastructure. It does not transfer responsibility for configuration. Your provider secures the platform; you secure how you use it. That division, usually called the shared responsibility model, is where most cloud incidents involving small businesses actually occur.
Recurring exposures:
Misconfigured sharing permissions, especially files or folders set to "anyone with the link" and then indexed or forwarded
Weak or absent MFA, particularly on administrator accounts and service accounts
Excessive privilege, where half the company has global admin because it was easier during setup
Forgotten accounts belonging to former staff, trials, or one-off projects
Stale integrations and OAuth grants, which are non-human identities with standing access that no password rotation ever touches. Sophos's 2026 identity research found external application permissions to be a contributing factor in more than half of the identity breaches reported.
Publicly accessible storage, including exposed buckets and open document links
Shadow IT, covered separately below
The good news is that the major platforms expose the controls you need, and the highest-value ones are free with your existing subscription. CISA's Secure Cloud Business Applications (SCuBA) guidance publishes concrete baseline configurations for Microsoft 365 and Google Workspace that a small business can work through in a day.
Ransomware
Ransomware reaches small businesses the same way everything else does: phishing, stolen credentials, exposed remote access, unpatched internet-facing software, and third-party connections. The shift worth noting is that it has become primarily an identity and email problem rather than a vulnerability problem. Sophos's 2026 survey found malicious email and phishing driving roughly half of incidents and identity-based factors implicated in the large majority of cases.
Two realities shape how you should prepare:
Extortion is increasingly about stolen data, not just encryption. Attackers exfiltrate first. Backups restore your operations; they do not un-publish your customer list. This is why prevention and detection still matter even with excellent backups.
Backups are targeted deliberately. Attackers look for backup infrastructure and destroy it before triggering encryption, because they know it determines whether you pay. Sophos's research has repeatedly found that organizations whose backups were compromised faced dramatically higher recovery costs, on the order of several times more than those with intact backups.
Meaningful controls, roughly in order of value: phishing-resistant MFA everywhere, no internet-exposed remote desktop, prompt patching of anything reachable from the internet, endpoint detection and response on every device, immutable or offline backup copies, restricted administrative privilege, and a recovery plan someone has actually tested.
Data Leakage
Not all data loss involves an attacker. In distributed teams, accidental exposure is at least as common as theft.
What tends to leak:
Customer records and contact databases
Financial statements, payroll files, banking information
Intellectual property, product roadmaps, pricing models
Employee personal data, including identity documents collected during hiring
Source code, configuration files, and infrastructure diagrams
API keys, tokens, and cloud credentials committed to repositories or pasted into tickets
Prompts and file uploads sent to consumer AI tools
How it leaks: over-permissive share links, files attached to the wrong thread, forwarding to personal email "to work on at home," exports to unmanaged devices, screenshots in public channels, departing employees copying their work, and misconfigured integrations that sync more than intended.
Treat accidental leakage as an engineering and process problem rather than a discipline problem. Default share settings, restrictions on external sharing, sensible retention, and least-privilege access prevent far more incidents than another reminder email.
Shadow IT
Shadow IT is the set of tools your team uses that you did not approve and do not know about. It is usually a symptom of friction: someone needed to sign a document, convert a file, transcribe a meeting, or automate a task, and the approved path was slow or nonexistent.
Typical categories include file-sharing sites, PDF and format converters, AI assistants and note-takers, project-management tools, browser extensions, personal cloud storage, automation platforms, and personal password managers holding business credentials.
The 2026 DBIR highlighted this trend specifically, reporting that employee use of unapproved AI tools roughly tripled to around 45%, with a corresponding spike in data leakage. Unapproved tools create three distinct problems: data lands somewhere with terms you never reviewed, access continues after the employee leaves because the account is personal, and you cannot investigate an incident involving a system you did not know existed.
The answer is rarely a blanket ban, which simply drives usage underground. It is a short approved-tools list, a genuinely fast approval route for additions, and periodic review of OAuth grants and expense reports to see what people are actually using.
Build a Risk-Based Cybersecurity Strategy
Small businesses get into trouble by buying tools before deciding what they are protecting. The result is a subscription pile that nobody has configured, nobody monitors, and nobody can explain.
A better approach borrows the structure of the NIST Cybersecurity Framework without the enterprise overhead. Five questions, answered honestly:
IDENTIFY — What do we have, what matters most, and who can reach it? An inventory of your data, applications, devices, and people. This is unglamorous and it is the single highest-return hour you will spend.
PROTECT — What controls reduce the likelihood that something goes wrong? MFA, patching, least privilege, encryption, training, secure configuration.
DETECT — How would we notice? Alerting on impossible-travel logins, new inbox rules, mass file downloads, MFA method changes, and endpoint alerts.
RESPOND — Who does what, in what order, at 11pm on a Friday? Named contacts, a contained set of first actions, and the authority to disable accounts without waiting for a meeting.
RECOVER — How do we get back to work, and how quickly? Tested restores, documented rebuild procedures, and communication plans for customers and regulators.
A five-person company can complete a credible version of all five in a couple of working days. The framework is not a compliance exercise; it is a way to stop spending on the wrong layer.
Security Area | Business Question | Recommended Action |
|---|---|---|
Identity | Who can access our systems, and how do they prove it? | Phishing-resistant MFA, centralized identity provider, no shared logins |
Devices | Which devices touch company data, and are they healthy? | Device inventory, enforced updates, encryption, endpoint protection |
Data | What would hurt most if it leaked, and where does it live? | Classification, least-privilege access, sharing restrictions |
Applications | Which SaaS tools are approved, and what can they reach? | Application inventory, OAuth review, offboarding checklist |
Monitoring | How would we find out something is wrong? | Enable audit logging, configure alerts, assign someone to read them |
Recovery | What happens the morning after an incident? | 3-2-1 backups with an isolated copy, tested restores, written playbooks |
Work down this table in order. Identity first, always. It produces more risk reduction per hour invested than anything else available to a small business.
Identity Should Become the New Security Perimeter
Identity-centric security means access decisions are made based on who is asking, what they are using, and what they are asking for, rather than where the connection originates.
The components are simpler than the jargon suggests:
User identity — the account representing a person, ideally one account per person, held in a single system of record.
Device identity — a known, registered, healthy machine. A login from a recognized company laptop is a materially different event from the same credentials arriving from an unknown device.
Authentication — proving the identity. This is where MFA and passkeys live.
Authorization — what that proven identity is permitted to do, which is a separate decision from authentication and frequently neglected.
Least privilege — the default should be the minimum access needed for the role, expanded deliberately rather than granted preemptively.
Conditional access — rules that evaluate signals before granting entry: device compliance, location, risk score, sensitivity of the application.
Role-based access control — permissions attached to roles rather than individuals, so that adding and removing people is a two-minute job.
Identity provider and single sign-on — one place where accounts are created, MFA is enforced, and, critically, access is revoked. SSO's underrated benefit is not convenience; it is that disabling one account closes every connected door at once.
For a remote team this matters more than for a co-located one because identity is the only consistent control point you have. You do not control the network. You may not fully control the device. You definitely control who gets an account and what that account can do.
Practical starting point for a small business: pick Microsoft Entra ID or Google Workspace as the single identity source, connect every SaaS tool that supports SSO, eliminate local accounts wherever possible, and maintain a list of the tools that cannot federate so you know where your gaps are.
Make Multi-Factor Authentication Mandatory
MFA is the highest-value control available to a small business, and the qualifier matters: not all MFA is equal, and MFA reduces account compromise substantially but does not eliminate it. Adversary-in-the-middle phishing kits and session-cookie theft both defeat traditional second factors.
Ranked from strongest to weakest:
Method | How it works | Phishing-resistant? | Practical notes |
|---|---|---|---|
Hardware security key (FIDO2) | Cryptographic proof bound to the site's origin | Yes | ~$25–60 per key; best for admins and finance. Issue two per person |
Passkey | Same FIDO2 cryptography, stored on a phone, laptop, or in a synced keychain | Yes | Free, built into modern devices, increasingly supported by major SaaS |
Authenticator app with number matching | Time-based code or a prompt requiring you to type a displayed number | Partially | Good baseline; number matching blocks blind approval of push fatigue |
Push approval (simple approve/deny) | Tap to approve | No | Vulnerable to MFA fatigue attacks; enable number matching if available |
One-time code via email | Code sent to a mailbox | No | If the mailbox is compromised, so is the factor |
SMS code | Code by text | No | Vulnerable to SIM swap and real-time relay. Better than nothing, worse than everything else |
Prefer phishing-resistant methods where the platform supports them. Passkeys have moved from novelty to mainstream: the FIDO Alliance reported in May 2026 that roughly five billion passkeys are in use globally and that about 68% of surveyed organizations have deployed or are deploying them for employee sign-in. For a small business this matters because it is now realistic to require passkeys for your core platforms without a procurement project. CISA maintains straightforward guidance on phishing-resistant MFA if you want the technical rationale.
MFA implementation checklist for a small business
Inventory every system holding company data, including the small ones
Enable MFA on the identity provider first (Microsoft 365 / Google Workspace)
Enforce it for administrators before anyone else, with security keys or passkeys
Turn on number matching and disable simple approve/deny push where possible
Remove SMS as a permitted method once stronger options are registered
Require at least two registered methods per person, so one lost phone is not a lockout
Generate recovery codes, print them, and store them somewhere physically secure
Block or restrict legacy authentication protocols that bypass MFA entirely
Define a help-desk identity-verification procedure for resets (a live video call or manager confirmation, never security questions over email)
Alert on MFA method changes and new device registrations
Review enrollment coverage monthly until it is 100%, then quarterly
That last item catches the most common failure: MFA that is enabled but not enforced, leaving a handful of accounts quietly exempt.
Create a Strong Password and Passkey Strategy
Passwords remain the fallback for every system that does not yet support passkeys, which is still most of them.
What actually works:
Unique credentials everywhere. Reuse is the single behavior that converts someone else's breach into yours.
A password manager for the whole company. Business tiers cost a few dollars per user per month and solve four problems at once: generation, storage, sharing, and visibility. They give you shared vaults with proper access control, so the Wi-Fi password and the shared marketing account stop living in a pinned Slack message.
Length over complexity. Current NIST digital identity guidance favors long passphrases and advises against mandatory periodic rotation and forced composition rules, which push people toward predictable patterns. Screen against known-breached password lists instead.
Rotate on evidence, not on schedule. Change credentials when there is a breach, a departure, a suspicion, or a shared secret that has been exposed. Arbitrary 90-day cycles mostly produce
Summer2026!followed byAutumn2026!.Breach monitoring. Most business password managers and identity platforms flag credentials appearing in known breaches. Turn it on and act on the alerts.
No password sharing between people. If two people need access, they need two accounts. Where a platform genuinely only supports one login (this is common in small-business banking and social media), use a shared vault entry with restricted membership, log who has access, and change it immediately when anyone with access leaves.
Passkeys wherever offered. Enable them for your identity provider, your banking, your domain registrar, and your code repositories first. Your registrar deserves particular attention; whoever controls your DNS controls your email.
A password manager makes sense for a small business the moment you have more than about three people or more than about ten business accounts, which in practice means almost immediately. The cost is trivial compared with a single compromised account.
Secure Every Employee Device
Devices are where credentials get stolen, where data is stored offline, and where ransomware executes. A remote workforce needs device security that works without anyone physically touching the machine.
Endpoint security checklist
Automatic operating-system updates enabled and verified, not merely available
Third-party application updates handled (browsers, PDF tools, collaboration apps)
Endpoint protection installed and reporting to a central console
Full-disk encryption on (BitLocker, FileVault, or the platform equivalent) with recovery keys escrowed centrally
Screen lock after five minutes, password or biometric required on wake
Local administrator rights restricted; daily work happens in a standard account
Host firewall enabled
Browser extensions reviewed and restricted to an allowed list where feasible
Device enrolled in management (Intune, Jamf, Google endpoint management, or similar)
Device inventory maintained: who has what, serial numbers, OS version, last check-in
Lost or stolen device procedure documented and known to staff
Remote lock and wipe capability configured and tested once
End-of-life plan: devices wiped and certificates revoked at retirement
Understanding what you are buying
The terminology in this market is deliberately blurry. The practical distinction:
Technology | What it does | Realistic limits | Small-business fit |
|---|---|---|---|
Antivirus | Matches files against known malicious signatures and basic heuristics | Weak against novel malware, fileless attacks, and credential theft | Minimum baseline; built-in options are now reasonable |
Endpoint protection platform (EPP) | Adds behavioral analysis, exploit mitigation, web filtering, device control | Prevention-focused; limited forensic visibility | Good default for most small businesses |
Endpoint detection and response (EDR) | Records endpoint activity, detects attacker behavior, enables investigation and remote isolation | Generates alerts that someone has to interpret and act on | Worth it once you have sensitive data or 20+ endpoints, provided someone will watch it |
Managed detection and response (MDR) | EDR plus a 24/7 human team doing the watching and initial response | Ongoing cost; you are trusting an external team | The realistic answer for a small business that wants detection without hiring a security analyst |
Be honest about the last column. EDR bought and ignored is worse than EPP configured properly, because it creates a false sense of coverage. If nobody will look at alerts at 2am, buy the managed version or do not buy it yet.
Establish a Remote Device Policy
Policy is not paperwork for its own sake. It is the document that makes expectations enforceable and decisions consistent when someone leaves, loses a laptop, or asks to use a personal machine.
Keep it to two or three pages. Cover:
Approved devices — which devices may access company data, and which systems are restricted to company-owned hardware
Personal-device requirements — the minimum bar for BYOD, and what the company can and cannot see or wipe
Minimum OS versions — supported releases only; a named date by which unsupported systems must be upgraded
Security updates — automatic installation required; a maximum window for critical patches
Encryption — required on all devices storing or accessing company data
Screen locking — timeout and authentication requirements
Local storage — what may be stored locally and what must stay in approved cloud systems
Removable media — whether USB storage is permitted, and any encryption requirement
Software installation — approval process for new applications and browser extensions
Lost or stolen devices — who to contact, how quickly, and what happens next
Work locations — expectations around public networks, shared spaces, screen privacy, and any restrictions on working from other countries (which can carry tax and data-residency implications)
Device retirement — return, wipe, and data-removal requirements at offboarding or refresh
Sample policy framework
1. Scope. Applies to all employees, contractors, and anyone accessing company systems. 2. Device standards. Company-owned laptops are issued to all employees. Personal devices may access email and chat only, and only when enrolled and meeting the compliance baseline in section 3. 3. Baseline. Supported operating system, current security updates, disk encryption enabled, screen lock at five minutes, approved endpoint protection, no jailbreaking or rooting. 4. Prohibited. Disabling security software, installing unapproved applications on company devices, storing customer data outside approved systems, sharing devices with family members while signed into company accounts. 5. Reporting. Loss, theft, or suspected compromise must be reported to [named contact] within two hours, by phone if systems are inaccessible. Reporting quickly will never result in disciplinary action. 6. Departure. Company devices returned within five business days. Access to all systems revoked on the final working day. Work profiles removed from personal devices. 7. Acknowledgement. Signed at onboarding and reconfirmed annually.
Section 5 does more work than it appears to. Employees who fear blame delay reporting, and delay is the most expensive variable in incident response.
Secure Home Wi-Fi and Remote Connections
Set expectations that employees can actually meet:
Use WPA2 or WPA3 encryption on the home network. WEP and open networks are unacceptable.
Change the router's default administrator password. Default credentials for consumer routers are published and trivially searchable.
Keep router firmware updated, or enable automatic updates if the model supports them. Replace hardware that no longer receives security updates.
Use a strong, unique Wi-Fi password and avoid sharing it broadly.
Consider a separate network for IoT devices if the router supports guest networks. Helpful, not mandatory.
On public Wi-Fi, prefer a phone hotspot. If you must connect, do not dismiss certificate warnings, and avoid administrative tasks.
Secure DNS (DNS over HTTPS, or a filtering resolver pushed to managed devices) blocks a useful slice of phishing and malware domains at low cost.
On VPNs, specifically
A VPN is a tunnel. It encrypts traffic between a device and a network endpoint. That solves exactly one problem: protecting traffic from observation or tampering on an untrusted local network. It is useful when you need to reach an internal system that is not published to the internet, when you need traffic to originate from a specific network, or when you genuinely do not trust the local link.
A VPN does not verify who is connecting, check whether the device is healthy, stop phishing, prevent malware, protect SaaS applications that are on the public internet anyway, or limit what an authenticated user can reach. Consumer VPN services do even less for a business; they change which company can observe your DNS queries and little else.
For a remote small business whose systems are all SaaS, a VPN is often unnecessary, and a traditional always-on VPN can actively hurt you by creating a flat internal network where one compromised laptop reaches everything. Identity controls, device compliance, application-level access, and endpoint protection deliver more protection for the same money. Keep a VPN where you have legacy internal systems, and consider replacing it with a zero-trust access service if and when budget allows.
Use Zero Trust Principles for Remote Teams
Zero Trust is a design principle, not a product, despite what the marketing suggests. In plain terms: stop granting access because of where a request comes from, and start granting it based on verified identity, device health, and the specific resource being requested, re-evaluated over time.
The principles that matter for a small business:
Never trust a connection automatically. Being "on the VPN" or "in the office" is not evidence of anything.
Verify the identity every time, with strong authentication.
Verify device posture where you can. Is this a known, encrypted, patched, protected device?
Apply least privilege. Access to the specific application or dataset, not to the whole environment.
Limit blast radius. Separate administrative accounts from daily-use accounts. Separate production from everything else.
Re-evaluate continuously. Session lifetimes, re-authentication for sensitive actions, revocation when risk signals appear.
You do not need to buy an architecture to apply these. A realistic small-business version, achievable with tools you likely already pay for:
All applications behind a single identity provider with MFA enforced
Conditional access rules requiring compliant or registered devices for sensitive applications
Separate admin accounts, used only for administration, protected with hardware keys
Access granted by role, reviewed quarterly
Sessions that expire, and a documented one-click way to revoke all sessions for a user
No flat internal network where everything can reach everything
That is Zero Trust in substance. CISA's Zero Trust Maturity Model is a useful reference if you want to understand where you sit and what maturing looks like, without committing to an enterprise rollout.
Control Access to Business Applications
Access control is where small businesses drift fastest. Permissions are granted during a busy week and never revisited.
Build the discipline around a few habits:
Role-based access. Define four to six roles and attach permissions to them. When someone joins, you assign a role rather than reconstructing permissions from memory.
Least privilege by default. Start narrow and widen on request. The reverse never happens.
Provisioning at onboarding. A written checklist of accounts to create, keyed to the role.
Offboarding on the day of departure. Disable the identity account first; SSO makes that one action close many doors. Then revoke sessions, transfer file ownership, remove from shared vaults, and reclaim devices.
Separate administrative accounts. Your global admin credential should not be the one you read email with.
Just-in-time privilege where supported. Elevate for a task, then drop back down.
No shared accounts except where a platform forces it, and then with a controlled vault entry.
Quarterly access reviews. Export the user list from each major system and confirm each entry is a current person who still needs it. This takes an hour and reliably finds surprises.
Worked example: access by role in a 20-person professional-services firm
Role | Should have | Should not have |
|---|---|---|
Founder / Director | Business overview, finance approval, delegated admin only when needed | Standing global admin on daily account; direct database access |
Finance | Accounting platform, banking, payroll, invoicing, supplier records | Customer production systems, source code, marketing platforms, HR files beyond payroll |
Marketing | CMS, analytics, social scheduling, email platform, design tools | Customer financial data, payroll, admin consoles |
Developer | Code repositories, staging environments, CI/CD, error monitoring | Standing production database access (request it, time-boxed, logged), finance systems |
Contractor | One project workspace, specific shared folders, time-limited | Everything else; access expires automatically at contract end |
Notice that the founder's row restricts rather than expands. Executive accounts are the most phished and most valuable, and standing global admin on an account used for daily email is a common and avoidable weakness.
Secure Microsoft 365, Google Workspace, and Other SaaS Platforms
Both major platforms are capable of being configured securely and capable of being configured badly. The differences that matter in practice are about which controls you have enabled, not which vendor's logo is on the tab.
Work through this list for whichever you use:
MFA enforced for every account, including service and shared mailboxes
Administrator accounts separated from daily accounts, protected with hardware keys, and limited in number (two or three is right for most small businesses; one is a lockout risk)
Break-glass account with a long stored credential, excluded from conditional access, monitored for use
Recovery settings verified: backup email and phone accurate, recovery codes stored offline
External sharing restricted to specified domains or requiring authentication, with link defaults set to "people in your organization"
Guest access reviewed periodically; external collaborators accumulate
Third-party application access controlled. Require admin consent for new OAuth apps and audit existing grants. This is one of the most overlooked controls in small-business SaaS.
Legacy authentication blocked (IMAP, POP, SMTP basic auth), which is the standard MFA bypass
Audit logging enabled and retained for a meaningful period. Verify your subscription tier actually retains logs long enough to investigate something discovered a month later.
Alerts configured for suspicious sign-ins, mass downloads, new inbox forwarding rules, and MFA method changes. Inbox rule creation is the classic BEC tell.
Account lifecycle managed: joiners, movers, leavers, with a defined process for each
Data retention and litigation hold configured as appropriate for your obligations
CISA's SCuBA baselines give you a vendor-neutral configuration target for both platforms, which is more useful than trying to derive best practice from the admin console yourself.
One more thing worth saying plainly: cloud providers replicate your data for availability, which is not the same as backing it up. If a user deletes a folder or ransomware encrypts synced files, native retention windows may or may not save you. Many small businesses add a third-party SaaS backup for this reason.
Protect Business Data Wherever It Travels
Data in a remote company moves through a chain: device → cloud platform → employee → customer → vendor. Each hop is a place it can be exposed.
Classification. You do not need an elaborate scheme. Three tiers is plenty:
Tier | Examples | Handling |
|---|---|---|
Public | Marketing material, published content | No restriction |
Internal | Project plans, internal docs, team communications | Company accounts only, no external sharing by default |
Confidential | Customer records, financials, contracts, credentials, source code, personal data | Named access only, external sharing blocked or requiring approval, encrypted at rest, retained per policy |
Encryption. In transit (TLS, which is largely automatic now) and at rest (disk encryption on devices; provider-managed encryption in cloud platforms). Encryption protects against device theft and physical access. It does not protect against a logged-in attacker, which is why access control matters more.
Access control. The operating principle:
Employees should have access to the information they need to do their jobs, not automatically to everything the company owns.
Secure sharing. Prefer named-recipient links over open ones, set expiry dates on external shares, and use view-only permissions when editing is not required.
Retention and deletion. Data you no longer hold cannot be stolen. Set retention periods, delete old exports, and remove customer data you have no continuing reason to keep. This is both a security control and, in many jurisdictions, a legal obligation.
Sensitive information handling. Define explicitly where things like identity documents, payment card data, and health information may be stored, who may access them, and how they are disposed of. If you handle payment cards, keeping them out of your environment entirely by using a compliant processor is dramatically cheaper than securing them yourself.
Backups Are Part of Cybersecurity
Backups are the control that determines whether an incident is a bad week or an existential event. They belong in your security program, not just your IT housekeeping.
The 3-2-1 principle, and the modern addition: keep at least three copies of your data, on two different types of media, with one copy off-site. Because ransomware operators actively hunt backup infrastructure, add: one copy immutable or offline. Immutable means the backup cannot be altered or deleted for a defined retention period, even by an administrator account.
Key practices:
Cover everything that matters, including SaaS data. Microsoft 365 and Google Workspace are not backups of themselves.
Isolate backup credentials. Backup systems should not be reachable with ordinary domain or workspace admin credentials. This is the control that most often fails.
Encrypt backups and store the keys somewhere separate from the backup system.
Restrict who can delete or shorten retention, and alert when anyone tries.
Monitor backup success. A backup job that has silently failed for six weeks is a common and devastating discovery.
Know your RPO and RTO. How much data can you afford to lose (recovery point) and how long can you afford to be down (recovery time)? These two numbers drive every other backup decision.
And the point that catches people out:
"We have backups" is not the same as "we can recover."
Backups fail to deliver recovery for predictable reasons: the restore was never tested, the restore takes eleven days over a slow connection, the backup covered the file server but not the database, the encryption key was stored in the system that got encrypted, or the backups themselves were encrypted because they were reachable with the same credentials as everything else.
Backup testing checklist (quarterly)
Restore a single file and confirm contents are correct and current
Restore a full system or virtual machine to an isolated environment
Time the restore end to end and compare against your stated RTO
Verify the restored data opens in the applications that use it
Confirm the immutable or offline copy exists and is within retention
Confirm backup admin credentials are separate and MFA-protected
Verify at least one restore from the off-site copy, not only the local one
Document who performed the test, when, and what failed
Fix what failed and retest
Build a Security-Aware Remote Workforce
An annual slide deck does not change behavior. The DBIR has consistently found the human element present in the large majority of breaches, around 62% in the 2026 edition, which tells you where the leverage is.
What works better than annual training:
Short and frequent. Ten minutes a month beats ninety minutes a year. Attention and recall both favor spacing.
Specific to your business. Use your actual tools, your actual suppliers, your actual payment process. Generic phishing examples teach generic lessons.
Timely. When a real phishing attempt hits your inbox, share a redacted version that day. Nothing lands like a live example.
Role-targeted. Finance needs payment-fraud depth. Developers need secrets management. Everyone needs phishing and reporting.
Practical, not theoretical. "Here is how to check where a link goes on a phone" is more useful than "be vigilant."
Topics to cover across a year: phishing and link inspection, social engineering by phone and chat, password manager use, MFA fatigue and why you never approve an unexpected prompt, invoice and payment fraud, executive impersonation, safe data sharing, AI tool risks, physical security while traveling, and how to report.
Blame-free reporting is the highest-leverage cultural control you have.
The economics are straightforward. An employee who reports a mistake in five minutes gives you a containable incident. An employee who hides it for three days gives you a breach. Fear produces delay, and delay is expensive.
Make it concrete:
Say explicitly, in writing, that reporting a suspected mistake will never lead to discipline
Provide a single, obvious reporting route: a "report phishing" button, an email alias, and a phone number for when systems are down
Acknowledge every report quickly, even the false alarms, and especially the false alarms
Thank people publicly for catching things, including the ones that turned out to be harmless
Measure the reporting rate as a positive metric. Rising reports mean the culture is working, not that you are under attack
Run occasional phishing simulations, but treat them as a measure of your program rather than a test of individuals. Never publish or penalize individual click rates. The goal is to find the gaps in your controls and training, not to shame the person who was moving fast on a Friday afternoon.
Security Training Should Reflect Real Remote Work
Abstract advice fails under pressure. Walk your team through scenarios they will plausibly encounter.
Scenario 1: An urgent payment-change request appearing to come from the CEO
The message: "I'm in back-to-back meetings. Our supplier updated their bank details, can you push this payment through today? Details attached. Don't loop in the team yet, we're still finalizing."
The risk: Business email compromise. Funds leave, and recovery depends on acting within hours.
What the employee should do: Do not reply to the message. Verify through an independent channel using a phone number you already have, not one in the email. If the CEO is unreachable, the payment waits. Urgency and secrecy together are the signature of this attack.
What the company should have configured: A written payment-verification rule requiring voice confirmation for any bank-detail change, a second approver for payments above a threshold, external sender warnings on email, DMARC enforcement on the domain, and a standing policy that no legitimate request will ever ask someone to bypass verification.
Afterwards: If a payment went out, contact the bank immediately and file with law enforcement (in the US, the IC3 recovery process is most effective within the first 24 to 72 hours). Then check whether the mailbox involved was compromised or whether the domain was merely spoofed, because those lead to very different follow-up actions.
Scenario 2: A Microsoft 365 login warning
The message: "Unusual sign-in detected. Verify your account within 24 hours to avoid suspension," with a link to a convincing login page.
The risk: Credential phishing, often through a proxy that captures the password, the MFA code, and the session cookie together.
What the employee should do: Do not use the link. Open the application directly from a bookmark or type the address. If you already entered credentials, report it immediately and say so plainly, then change the password and expect IT to revoke sessions.
What the company should have configured: Phishing-resistant MFA, a report-phishing button, alerts on impossible-travel and anomalous sign-ins, and the ability to revoke all sessions for a user in one action.
Afterwards: Reset credentials, revoke all active sessions and refresh tokens, review MFA methods for anything newly registered by the attacker, check for new inbox rules and forwarding, and review mailbox and file access logs for the exposure window.
Scenario 3: A customer spreadsheet uploaded to a consumer AI tool
The situation: An employee pastes a customer export into a free AI chatbot to summarize it, using a personal account.
The risk: Personal data disclosed to a third party under consumer terms, potentially retained or used for training, outside any agreement you have with your customers. Depending on your jurisdiction and the data type, this may be a reportable event.
What the employee should do: Report it the same day. Delete the conversation and the data from the tool where possible. Do not quietly hope it is fine.
What the company should have configured: An approved-AI-tools list, business-tier accounts with training disabled and appropriate data terms, a written rule on what data may never be pasted into any AI tool, and a fast route to request new tools so people are not improvising.
Afterwards: Assess what was exposed and whether notification obligations are triggered. Review the vendor's retention and deletion options. Ask why the approved path was not available, and fix that.
Scenario 4: A laptop lost while traveling
The situation: A bag is taken from a café in another city. The laptop was closed but not shut down.
The risk: If encryption is off, all local data is readable. If a session was live, active sessions may be usable.
What the employee should do: Report within the hour by phone if necessary. Note the last location and whether it was locked.
What the company should have configured: Full-disk encryption with escrowed recovery keys, short screen-lock timeouts, device management with remote lock and wipe, and a device inventory so you know exactly what was on it.
Afterwards: Remote lock, then wipe. Revoke sessions and rotate credentials that were stored or cached. Remove the device from conditional access. Document the data that was present and assess exposure. File a police report if required for insurance or notification purposes.
Scenario 5: A contractor's access remains active after the project ends
The situation: A freelance developer finished three months ago. Their account still has repository access and a valid API key.
The risk: Access outside any current agreement, on a device you do not manage, with credentials that may be reused elsewhere or sold. If that account is later compromised, the intrusion arrives through a trusted identity.
What should happen: Access should have expired automatically at the contract end date.
What the company should have configured: Time-bound accounts with expiry dates set at creation, a contractor offboarding checklist, key rotation at project end, and a quarterly access review that catches what the process missed.
Afterwards: Revoke the account and rotate every key it touched. Review logs for activity since the project ended. Add the gap to your offboarding checklist so it does not recur.
Protect Email From Business Email Compromise
Email is the highest-loss attack surface for small businesses, and BEC is the highest-loss category within it. Because BEC frequently arrives with no link, no attachment, and no malware, technical filtering alone cannot solve it.
Email authentication, explained plainly
SPF (Sender Policy Framework) is a published list, in your DNS, of the servers permitted to send email for your domain. A receiving server checks whether the sending server is on the list.
DKIM (DomainKeys Identified Mail) adds a cryptographic signature to outgoing messages, letting receivers verify the message genuinely came from your domain and was not altered in transit.
DMARC (Domain-based Message Authentication, Reporting and Conformance) ties the two together. It tells receiving servers what to do when a message claiming to be from you fails those checks (do nothing, quarantine, or reject) and sends you reports about who is sending mail as your domain.
Deploy all three, and move DMARC to an enforcement policy rather than leaving it at p=none, which only generates reports. Start in monitoring mode, read the reports for a few weeks to identify legitimate senders such as your invoicing and marketing platforms, then tighten to quarantine and finally reject.
What these protocols do and do not do: they make it much harder for someone to spoof your exact domain. They do nothing about a lookalike domain (yourcornpany.com), nothing about a free webmail account using your CEO's display name, and nothing about an email sent from a genuinely compromised mailbox at one of your suppliers, which is authenticated perfectly because it is real. Treat authentication as necessary and insufficient.
The rest of the email defense stack
MFA on every mailbox, phishing-resistant for finance and executives
Block legacy authentication protocols that bypass MFA
Alert on inbox rule creation and mail forwarding. Attackers create rules to hide their tracks; this is one of the most reliable compromise indicators available to a small business
External sender warnings on inbound mail from outside the organization
Lookalike domain monitoring, and registering the two or three most obvious typo variants of your own domain
Display-name impersonation rules flagging external mail using internal names
Payment verification procedure, written down and applied without exception: any change to bank details requires voice confirmation on a previously known number, and any payment over a defined threshold requires a second approver
Supplier notification protocol so your customers know you will never change bank details by email alone
That payment procedure is the actual control. Every technical measure above exists to reduce how often it gets tested.
Manage Third-Party and Contractor Access
Third-party access is one of the fastest-growing risk categories. The 2026 DBIR found third-party involvement in roughly 48% of breaches, a sharp rise driven by vendor compromise, cloud platform access, and application integrations.
For a small business the exposure comes from freelancers, agencies, outsourced developers, consultants, bookkeepers, SaaS vendors, and managed service providers. Each is a legitimate identity in your environment that you do not control.
A practical access lifecycle
Request → Approve → Provision → Monitor → Review → Revoke
Request. Who needs access, to what specifically, why, and until when. An end date is mandatory, not optional.
Approve. One named person approves. For anything touching customer data or production, require a written agreement covering confidentiality, security expectations, and breach notification.
Provision. Create a named individual account, never a shared one. Grant the minimum required. Set the expiry date at creation, so that revocation is the default outcome rather than a task someone must remember.
Monitor. Third-party activity should appear in your audit logs and be distinguishable from employee activity.
Review. Every quarter, list all external identities and confirm each is still needed. Include OAuth application grants; they are third-party access too.
Revoke. At project end or contract termination, disable the account, rotate any shared credentials or API keys, remove from shared vaults and channels, and confirm rather than assume.
For your vendors, ask a short set of questions before granting access or sending data: Do you enforce MFA for your staff? How is our data encrypted and where is it stored? Who on your side can access it? What is your breach notification commitment and timeline? Can you provide a SOC 2 report or equivalent? Do you subcontract any part of this? Five questions answered badly tell you a lot.
The principle to hold onto: temporary access must expire by default. Anything else becomes permanent through inattention.
Secure Remote Development Teams
If your business writes software, your developers hold the most powerful credentials in the company and often work on the least restricted machines.
The specific risks:
Source code repositories containing business logic, customer data in test fixtures, and infrastructure configuration
API keys and cloud credentials hardcoded into code, committed to git history, pasted into chat, or left in local
.envfilesSecrets in CI/CD pipelines, which typically hold production credentials and can be triggered by anyone who can merge code
SSH keys without passphrases, copied between machines, and rarely rotated
Production access granted permanently for convenience during an incident two years ago
Open-source dependencies, including typosquatted packages and compromised maintainer accounts
Developer laptops with local admin rights, many tools, and broad network access
Controls that fit a small team:
Enforce MFA and require signed commits on your code platform; protect the main branch with required reviews
Use a secrets manager (your cloud provider's, or a dedicated tool) so that credentials are never in code, chat, or documents
Turn on automated secret scanning in repositories, and treat any exposed key as compromised: rotate immediately rather than deleting the commit, because git history persists and scrapers are fast
Separate environments properly. Development and staging should not hold real customer data, and should not have credentials that work in production
Make production access time-bound and logged. Request, approve, expire
Pin dependencies, enable automated dependency alerts, and review what your build pipeline is allowed to do
Scope CI/CD credentials narrowly; use short-lived tokens through OIDC federation rather than long-lived static keys where your platform supports it
Apply the same device standards to developer laptops that you apply to everyone else
OWASP publishes free, practical guidance on application and pipeline security that is well suited to small teams without a security engineer.
The behavioral rule worth stating in your engineering handbook: production credentials never live in code, documents, tickets, chat messages, or unencrypted local files. If one currently does, rotate it today.
Address the Security Risks of AI Tools in Remote Work
AI assistants are now embedded in daily work at small companies, used for writing, research, coding, marketing copy, customer support drafts, data analysis, meeting transcription, and general productivity. This is a genuine productivity gain, and the security question is not whether to allow it but how.
The DBIR's finding that unapproved AI use roughly tripled to around 45% of employees, with an associated spike in data leakage, describes most small businesses accurately. People are using these tools whether or not anyone approved them.
The real risks
Confidential data in prompts. Contracts, financials, strategy documents, and customer records pasted into consumer tools governed by consumer terms.
Personal data disclosure. Uploading customer records to a third party you have no data processing agreement with can breach both your privacy obligations and your customer contracts.
Source code exposure, including proprietary logic and embedded credentials.
API keys and secrets pasted into a chat window while debugging.
Meeting transcription tools that join calls as participants and retain recordings of sensitive discussions, often invited by one person on behalf of everyone.
Unapproved AI applications with broad OAuth permissions to your mailbox, calendar, and drive.
Personal accounts, meaning the data and the history leave with the employee.
AI-assisted attacks against you: fluent phishing at scale, convincing voice cloning for phone-based fraud, and deepfake video in approval workflows.
Overtrust in output. Fabricated citations, incorrect legal or financial reasoning, and insecure generated code shipped without review.
Small Business AI Usage Security Policy (adaptable template)
1. Purpose. To let the team use AI tools productively while protecting customer data, company information, and legal obligations.
2. Approved tools. Only tools on the approved list may be used for company work. Current list: [tool, purpose, account type]. Requests for additions go to [contact] and will be answered within five business days.
3. Account requirements. Company work uses company-provisioned business or enterprise accounts only. Personal accounts must not be used for company data. Where the tier offers it, training on our data is disabled and retention is configured to the minimum available.
4. Data that must never be entered into any AI tool.
Customer personal data, including names combined with contact, financial, or health details
Payment card numbers, bank details, or credentials of any kind
API keys, tokens, passwords, or configuration secrets
Employee personal data, including identity documents and salary information
Signed contracts, legal advice, and anything under NDA
Unreleased financial results, strategy documents, or acquisition discussions
Proprietary source code, unless using an approved enterprise coding tool
5. Data that is acceptable. Public marketing material, general research questions, anonymized or synthetic examples, internal drafts containing no confidential specifics, and code in approved tools where the repository is already covered by the agreement.
6. Meeting assistants. AI notetakers may join internal meetings only, must be disclosed to all participants, and must not join client calls without written client consent.
7. Human review. AI output used in customer communications, contracts, financial analysis, or production code must be reviewed by a competent human before use. The employee remains accountable for accuracy.
8. Integrations. AI tools requesting access to email, calendar, files, or code require admin approval before connection.
9. Incident reporting. If confidential data is entered into a tool by mistake, report to [contact] the same day. Reporting will never result in disciplinary action. Late discovery of an unreported incident may.
10. Review. This policy is reviewed quarterly, because the tools change quickly.
Pair the policy with an approved tool that is actually good. The reason shadow AI thrives is that the sanctioned option is usually worse or absent. Give people something capable and the policy largely enforces itself.
Build a Small-Business Security Stack Without Overspending
Security spending should follow risk reduction, not vendor category. Here is a layered stack in the order most small businesses should build it.
Foundation (do this first; largely free or low cost)
MFA on every account, phishing-resistant for admins and finance
Business password manager for the whole team
Automatic OS and application patching, verified rather than assumed
Endpoint protection on every device, centrally visible
Backups with an isolated or immutable copy, plus one tested restore
Email authentication (SPF, DKIM, DMARC at enforcement)
Written policies: acceptable use, devices, AI, incident response
Identity (next, once the foundation holds)
A single identity provider as the source of truth
SSO for every application that supports it
Role-based access and removal of standing admin rights
Conditional access requiring compliant devices for sensitive applications
Quarterly access reviews and a written offboarding checklist
Visibility (you cannot respond to what you cannot see)
Audit logging enabled with adequate retention on all major platforms
Alerts configured for the handful of events that reliably indicate compromise: impossible-travel logins, new inbox rules, MFA method changes, mass downloads, new admin grants
Device inventory and compliance reporting
SaaS application inventory, including OAuth grants
A named person responsible for reviewing alerts, with a defined cadence
Advanced protection (when risk or growth justifies it)
EDR with a real response process, or MDR if nobody will watch it
Security awareness platform with phishing simulation
Third-party SaaS backup for Microsoft 365 or Google Workspace
Zero-trust network access replacing legacy VPN
Vulnerability scanning; CISA offers no-cost cyber hygiene scanning to eligible US organizations
SIEM or log aggregation, generally only once you have staff or a provider to use it
Cyber insurance, with the caveat that insurers now require most of the above as a condition of coverage
The right stack depends on headcount, data sensitivity, industry, regulatory obligations, cloud dependency, and technical maturity. A three-person design studio and a 40-person healthcare billing company should not own the same tools. Anyone selling you an identical answer for both is selling, not advising.
Cybersecurity Budget Planning for Small Businesses
Avoid rules of thumb that express security spending as a fixed percentage of revenue or IT budget. They are widely quoted and poorly supported, and they produce nonsense at small scale.
Budget instead against a tiered model.
Tier | What it covers | Typical position |
|---|---|---|
Must have | MFA, password manager, patching, endpoint protection, backups with tested restore, email authentication, basic training, written IR contacts | Non-negotiable at any size. Mostly included in subscriptions you already hold or costs a few dollars per user per month |
Should have | Device management, SSO, EDR, audit logging and alerting, security awareness platform, SaaS backup, documented policies | Appropriate once you exceed roughly 10–15 people or hold sensitive data |
Advanced | MDR, zero-trust network access, vulnerability management, cyber insurance, formal access reviews, tabletop exercises | Justified by regulated data, meaningful downtime cost, or customer security requirements |
Specialized | Compliance certification (SOC 2, ISO 27001), penetration testing, dedicated security staff, SIEM, virtual CISO | Driven by a specific obligation: enterprise customers, regulators, investors, or contractual commitments |
Factors that should move you up the tiers:
Headcount and device count. More people means more identities to manage and a real need for automation.
Data sensitivity. Health, financial, legal, or children's data raises both obligation and consequence.
Regulatory exposure. GDPR, HIPAA, PCI DSS, and sector rules impose concrete requirements.
Cloud dependency. If everything is SaaS, spend on identity and SaaS configuration rather than network gear.
Cost of downtime. Calculate what one day offline costs in revenue and payroll. Compare it with the annual cost of the control that would prevent it. This single calculation resolves most budget arguments.
Customer requirements. Enterprise clients increasingly mandate controls contractually; the cost is then a sales expense, not a security expense.
Existing capability. A team with technical staff can operate tools that a team without one should buy as a managed service.
The most common budgeting mistake is buying licenses and never completing configuration. An unconfigured tool provides zero protection and full cost. Before any new purchase, ask who will implement it, who will maintain it, and who will respond to what it produces. If those three answers are "nobody," buy something else or buy it managed.
Managed Security Services vs Internal IT
Most small businesses will use external help. The question is what kind.
Model | Strengths | Limitations | Suitable scenario |
|---|---|---|---|
Internal IT | Direct control, deep business context, immediate availability, no per-ticket friction | Security expertise is a separate discipline from IT; no 24/7 coverage; key-person risk | Businesses above roughly 40–50 staff, or with specific technical needs |
MSP (managed service provider) | Broad IT coverage at predictable cost, handles devices, help desk, and patching | Security depth varies enormously; many are IT providers with a security add-on; they become a high-privilege third party in your environment | Businesses without internal IT needing general coverage |
MSSP / MDR (managed security provider) | Genuine security specialization, 24/7 monitoring and response, threat intelligence | Costs more; needs your IT function to exist alongside it; can produce alerts you must still act on | Regulated industries, sensitive data, higher-value targets |
Hybrid | Internal ownership of strategy and context, external depth for monitoring and response | Requires clear boundaries and coordination, or things fall between the two | Growing businesses, and most 20–75 person companies |
Questions to ask any provider before signing
Which specific controls do you implement and monitor, and which remain our responsibility? Ask for this in writing.
What are your response time commitments, and what happens at 3am on a holiday?
Do you monitor identity events and SaaS platforms, or only endpoints and network?
How do you access our environment, and is that access MFA-protected and logged?
Will you respond to incidents or only notify us? This distinction is frequently blurred and materially changes the value.
Who owns the tooling and the data if we leave? Can we export our logs?
Can you provide a SOC 2 Type II report or equivalent?
What happened in your last customer security incident, and what changed afterwards?
That last question is worth asking directly. The answer, and the willingness to give one, is informative.
Remember that your MSP or MSSP holds privileged access to your environment. Attackers understand this and have repeatedly targeted providers as a route to many clients at once. Hold your providers to the standards you hold yourself, and make sure their access is scoped, MFA-protected, and reviewable.
Incident Response for a Remote Workforce
Speed determines cost. An account compromise contained in fifteen minutes is an inconvenience; the same compromise found three weeks later is a breach with notification obligations and customer damage.
Remote teams introduce specific complications: you cannot walk to the machine, the employee may be asleep in another time zone, the device may be personal, and the compromised communication channel may be the one you would normally use to coordinate.
A practical response sequence
Report. One known contact, one known method, plus a backup phone number for when email and chat are untrustworthy. Every employee should know this without looking it up.
Contain. Stop the bleeding before you understand it. Disable the account, revoke all sessions and refresh tokens, isolate the device through your management console. Containment precedes investigation.
Investigate. What was accessed, when, from where, and by whom? Check sign-in logs, inbox rules, forwarding, file access, OAuth grants, and MFA method changes. Preserve logs before retention windows close.
Reset and revoke. New credentials, re-registered MFA methods, rotated API keys and tokens, removed attacker persistence. Attackers routinely add their own MFA method; a password reset alone does not evict them.
Recover. Restore from clean backups, rebuild compromised devices rather than cleaning them, and verify integrity before returning systems to service.
Communicate. Internally first, then customers, partners, regulators, insurers, and law enforcement as required. Know your notification deadlines in advance; GDPR's 72-hour window for notifiable breaches does not pause while you decide.
Learn. A short written review within two weeks: what happened, what worked, what did not, and the three specific changes you are making. Assign owners and dates.
Prepare the boring parts in advance. Keep an offline copy of your incident contacts, your insurer's hotline, your provider's escalation path, and the account recovery procedures for your critical platforms. During a real incident you may not have access to the wiki where you filed them.
Create a Remote-Work Cybersecurity Incident Playbook
Playbooks let a non-specialist take correct first actions under stress. Keep each one to a single page.
Lost or Stolen Device
Employee reports immediately, by phone if systems are inaccessible. No blame, ever.
Record what happened: where, when, whether the device was locked, what was open.
Remote lock through the management console. Wipe if recovery is unlikely or the data is sensitive.
Revoke all active sessions and refresh tokens for that user.
Rotate credentials that were stored or cached on the device.
Remove the device from conditional access and your trusted device list.
Assess data exposure using your inventory of what was stored locally.
File a police report where required for insurance or notification.
Issue a replacement and confirm the baseline configuration before handover.
Compromised Account
Disable the account immediately. Do not start by asking the user questions.
Revoke every active session and refresh token. This is the step most often skipped, and skipping it means the attacker retains access despite the password change.
Reset the password and re-register MFA from scratch.
Review all authentication events: locations, devices, times, and any newly added MFA methods.
Check the mailbox for new inbox rules, forwarding addresses, and deleted items. Check for messages sent by the attacker.
Review file access and download activity for the compromise window.
Audit OAuth grants and connected applications for anything newly authorized.
Check whether the same credentials were reused on other systems, and reset those too.
Notify anyone who may have received messages from the compromised account.
Determine whether notification obligations are triggered, and document the decision either way.
Suspected Malware
Disconnect the device from the network. Do not power it off if you may need memory forensics; isolate through your management tool if available.
Contact IT or your security provider before doing anything else.
Do not attempt to clean or investigate the machine yourself. Well-meaning investigation destroys evidence and rarely removes a determined infection.
Preserve the device until advised.
Treat every credential entered on that device as compromised and rotate it.
Rebuild from a known-good image rather than cleaning, unless a specialist advises otherwise.
Check whether other devices show related indicators.
Restore data from backups taken before the suspected infection date.
Cybersecurity Compliance and Privacy
Compliance obligations depend on where you operate, what industry you serve, what data you hold, and what your customers require contractually.
Framework | Applies when | Core focus |
|---|---|---|
GDPR / UK GDPR | You process personal data of people in the EU or UK, regardless of where you are | Lawful basis, data minimization, individual rights, breach notification within 72 hours |
HIPAA | You handle US protected health information as a covered entity or business associate | Safeguards for health data, business associate agreements, breach notification |
PCI DSS | You store, process, or transmit payment card data | Cardholder data protection; scope shrinks dramatically if you use a compliant processor and never touch card data |
SOC 2 | Usually driven by enterprise customers rather than law | Independent attestation of controls over security, availability, and confidentiality |
ISO/IEC 27001 | Often required in international B2B contexts | Certified information security management system with continuous improvement |
Other regimes may apply: state privacy laws in the US, India's Digital Personal Data Protection Act, sector rules in finance and legal services, and increasingly, customer contracts that impose security terms more demanding than any regulation.
Two points that matter more than the list:
Compliance is a floor, not a ceiling. Frameworks describe a minimum acceptable standard, usually written several years ago, and they are assessed at a point in time. You can pass an audit in March and be compromised in April through something the audit never examined.
Security without compliance is possible; compliance without security is common. A business with strong MFA, tested backups, and managed devices but no certification is genuinely safer than one with a framed certificate and shared admin passwords.
Compliance ≠ Security.
Use frameworks as structure and as a sales enabler when customers require them. Do not mistake the certificate for the outcome.
Common Cybersecurity Mistakes Small Businesses Should Avoid
Mistake | Why it creates risk | What to do instead |
|---|---|---|
Relying only on antivirus | Signature matching misses credential theft, phishing, and identity attacks entirely, which is how most compromises now begin | Layer identity, device, email, and data controls; add EDR or MDR as you grow |
Shared passwords | No attribution, no selective revocation, and the credential is inevitably in a chat log | Individual accounts; a password manager with shared vaults for the genuine exceptions |
MFA enabled but not enforced | The exempt handful become the entry point | Enforce for everyone, audit coverage monthly, remove weak methods |
Permanent admin privileges | Any compromise of that account is a total compromise | Separate admin accounts, hardware keys, just-in-time elevation |
Never testing backups | Untested backups fail when it matters, and you discover it during the worst week of the year | Quarterly restore tests with documented results |
Ignoring offboarding | Live accounts belonging to departed people are unattributable access | Offboarding checklist executed on the final day, verified by access review |
Running unsupported software | No security patches means known exploits work indefinitely | Track end-of-life dates and budget for replacement before they arrive |
Uncontrolled SaaS adoption | Data in unknown systems, unrevokable access, no visibility during incidents | Short approved list, fast approval path, quarterly OAuth review |
Buying tools without configuring them | Full cost, zero protection, false confidence | Before purchase, name who implements, maintains, and responds |
Ignoring logs and alerts | Detection without response is just an expensive archive | Enable logging, configure a small number of high-value alerts, assign an owner |
Assuming the cloud provider handles everything | Shared responsibility means configuration, access, and data protection are yours | Work through your provider's security baseline explicitly |
Treating security as IT's problem | The controls that matter most (payment verification, data handling, access decisions) are business processes | Owner-level sponsorship, department-specific practices, security in onboarding |
Having no incident-response plan | Improvising at 2am produces slow, wrong decisions | One page per scenario, contacts stored offline, rehearsed once a year |
A Practical 30-60-90 Day Cybersecurity Plan
This roadmap assumes a small business starting from a low baseline, with a non-specialist owner or office manager driving it, perhaps five hours a week.
First 30 Days: Establish the Foundation
The objective is to close the gaps that attackers exploit most often.
Week 1. List every system holding company data, every person with access, and every device that touches it. Spreadsheet is fine. Identify your administrator accounts, including the ones you forgot about.
Week 1. Enable MFA on the identity provider and email for everyone. Start with administrators, using hardware keys or passkeys.
Week 2. Deploy a business password manager. Import existing credentials, identify reused and weak ones, replace them, and move shared secrets out of chat threads into controlled vaults.
Week 2. Verify automatic updates are enabled and actually installing on every device. Identify anything running an unsupported OS and plan replacement.
Week 3. Confirm backups exist for everything that matters, including SaaS data. Perform one restore test. Verify an isolated or immutable copy exists.
Week 3. Review every administrator account. Remove unnecessary ones, separate admin from daily accounts, and document the break-glass procedure.
Week 4. Run a 45-minute all-hands session covering phishing, MFA prompts, payment verification, and how to report. Communicate the blame-free reporting commitment explicitly.
Week 4. Write down your incident contacts, store an offline copy, and tell everyone where it is.
Days 31–60: Strengthen Controls
The objective is coverage and consistency.
Conduct a full access review across every system. Remove former employees, unused accounts, and permissions nobody can justify.
Deploy device management and enroll company devices. Enforce encryption, screen lock, and patch compliance.
Configure email security: SPF, DKIM, DMARC moved toward enforcement, external sender warnings, alerts on inbox rules and forwarding.
Work through the security baseline for your SaaS platforms: sharing defaults, external access, OAuth consent, audit logging, and alerting.
Classify your data into three tiers and adjust permissions on the confidential tier.
Write the offboarding checklist and use it for the next departure.
Draft the incident-response plan and the three playbooks in the section above.
Publish the AI usage policy and approve at least one genuinely useful tool.
Days 61–90: Improve Resilience
The objective is detection, verification, and sustainability.
Configure security alerting and assign a named person to review it on a defined schedule.
Run a vulnerability scan on anything internet-facing and remediate what it finds.
Run your first phishing simulation. Measure the reporting rate, not individual failures.
Perform a full backup recovery test and time it against your stated RTO.
Review third-party and contractor access. Revoke what has expired. Set expiry dates on what remains.
Formalize policies: acceptable use, devices, data handling, access control, incident response.
Run a one-hour tabletop exercise with the leadership team. Ransomware on a Friday afternoon is the classic scenario. CISA publishes tabletop exercise guidance to structure it.
Evaluate whether EDR, MDR, or cyber insurance is now justified by your risk and growth.
Schedule the recurring calendar items: monthly MFA coverage check, quarterly access review, quarterly backup test, annual policy review.
That last bullet is what separates programs that hold from projects that decay. Put the recurring tasks in a calendar with a named owner, or ninety days from now you will be back where you started.
Remote-Team Cybersecurity Checklist
Print this. Work through it. Date it and repeat quarterly.
Identity
MFA enabled and enforced on every account with no exemptions
Phishing-resistant methods (passkeys or security keys) for administrators and finance
Unique credentials on every system; no reuse
Business password manager deployed and adopted
Administrator accounts separated from daily-use accounts
Break-glass account documented, secured, and monitored
Access reviewed at least quarterly
Single identity provider with SSO wherever supported
Devices
Operating system updates automatic and verified
No devices running unsupported operating systems
Endpoint protection installed and centrally visible
Full-disk encryption enabled with recovery keys escrowed
Screen lock configured on laptops and phones
Device inventory current: owner, serial, OS, last check-in
Remote lock and wipe configured and tested once
Local admin rights restricted
Data
Sensitive data identified and classified
Sharing permissions reviewed; open links audited
External sharing restricted or requiring approval
Backups configured for all critical systems, including SaaS
Immutable or offline backup copy exists
Recovery tested in the last 90 days, with results documented
Retention and deletion schedules defined
Employees
Security training delivered in the last quarter
Phishing reporting mechanism available and known to all
Blame-free reporting stated in writing
Payment verification procedure documented and followed
AI usage policy communicated and acknowledged
Security covered in onboarding for new starters
Applications
SaaS inventory maintained
Unused accounts and trials removed
OAuth grants and connected apps reviewed
Admin consent required for new integrations
Legacy authentication protocols blocked
Audit logging enabled with adequate retention
Third Parties
All contractor and vendor access documented with expiry dates
Agreements in place covering confidentiality and breach notification
Provider access MFA-protected and logged
Expired access revoked and verified
Incident Response
Incident contacts documented and stored offline
Lost-device procedure written and accessible
Account-compromise procedure written and accessible
Session revocation process known and tested
Notification obligations understood in advance
Tabletop exercise run in the last 12 months
How to Measure Cybersecurity Progress
Counting tools measures spending, not security. Measure the things that describe your actual exposure and your actual ability to recover.
Metric | What good looks like | Why it matters |
|---|---|---|
MFA enrollment coverage | 100%, with phishing-resistant methods for privileged accounts | Exemptions are where attackers enter |
Managed device percentage | Approaching 100% of devices accessing company data | Unmanaged devices are invisible risk |
Patch compliance | Critical patches applied within 7–14 days | Exploitation timelines have compressed to days |
Backup success rate | 100%, monitored, with failures investigated | Silent failure is the default mode of backups |
Restore test success | At least one successful full test per quarter, timed | The only evidence that backups work |
Stale accounts | Zero accounts belonging to departed people | Unattributable standing access |
Time to revoke access after departure | Same day, ideally same hour | Measures whether offboarding is a process or a hope |
Phishing reporting rate | Rising over time; higher than click rate | The best proxy for security culture |
Training completion | 100% within 30 days of assignment | Table stakes, but track it |
Open critical vulnerabilities | Zero on internet-facing systems | Direct measure of exploitable surface |
Mean time to detect | Hours, not weeks | The variable that most determines cost |
Mean time to contain | Under an hour for account compromise | Containment speed caps the damage |
Unauthorized applications discovered | Declining, and discovered by you rather than during an incident | Measures shadow IT visibility |
Review five or six of these monthly. Pick the ones tied to your biggest risks, and improve them deliberately rather than tracking everything badly.
Security maturity is measured by risk reduction and demonstrated resilience, not by the number of products you have purchased.
What Small Businesses Should Prioritize First
If you can only do ten things, do these, roughly in this order:
Identity protection. One identity provider, one account per person, no shared logins.
Multi-factor authentication. Everywhere, enforced, phishing-resistant for privileged accounts.
Secure devices. Encryption, endpoint protection, management, and inventory.
Patching. Automatic, verified, and fast for anything internet-facing.
Backups. Covering SaaS, with an isolated copy, tested by restoring.
Least-privilege access. Roles, reviews, prompt offboarding.
Employee awareness. Frequent, specific, and blame-free.
Email security. Authentication, alerting on inbox rules, and a payment verification rule.
Incident response. Contacts, playbooks, and the ability to revoke sessions quickly.
Continuous improvement. Recurring reviews with named owners.
Treat this as a default rather than a law. A software company with a small production environment should move development and cloud security higher. A retailer handling card payments should prioritize scope reduction with a compliant processor. A consultancy whose main asset is client confidentiality should push data classification and third-party controls up the list. Your threat exposure and your business context determine the order; the list determines the content.
Cybersecurity for Remote Teams Is an Ongoing Process
There is no configuration you reach and then stop. Your team changes, your tools change, your data grows, and the techniques used against you change faster than any of it. The 2026 DBIR's observation that AI has compressed the interval between vulnerability disclosure and exploitation from months to hours is a good illustration: the same patching policy that was adequate two years ago is not adequate now, and nothing about your business changed.
Sustainable security for a small business looks like a small number of recurring commitments:
Monthly: MFA coverage check, patch compliance review, backup success verification, a short training moment
Quarterly: Access review across all systems, backup restore test, third-party and OAuth review, policy spot-check
Annually: Full policy review, tabletop exercise, vendor security review, insurance and coverage review, and an honest reassessment of whether your controls still match your risk
None of that requires an enterprise security department. It requires a named owner, a recurring calendar entry, and leadership that treats the time as non-negotiable.
Maturity comes gradually. Year one is getting the foundation right and making it stick. Year two is adding visibility and detection. Year three is resilience and, if your customers demand it, formal assurance. Companies that try to skip to year three usually end up with expensive tools sitting on a weak foundation, which is the worst of both outcomes.
Frequently Asked Questions
1. What is the biggest cybersecurity risk for small businesses with remote employees?
Compromised identities. An attacker with valid credentials for your email or identity provider does not need malware, does not need to breach a network, and often does not trigger any alert. Phishing and infostealer malware are the main routes in, and the consequences typically follow as business email compromise, data theft, or ransomware. This is why MFA, and ideally phishing-resistant MFA, is the highest-value control available to a small business.
2. How can a small business secure remote workers on a limited budget?
Start with controls that are free or nearly free in subscriptions you already pay for: enforce MFA everywhere, enable automatic updates, turn on disk encryption, configure backups with one isolated copy, set restrictive sharing defaults in your cloud platform, and enable audit logging and a handful of alerts. Add a business password manager for a few dollars per user per month. Those steps eliminate the majority of realistic attack paths before you spend on security products.
3. Is a VPN enough to protect remote employees?
No. A VPN encrypts traffic between a device and a network endpoint. It does not verify who is connecting, check whether the device is healthy, stop phishing, block malware, or protect SaaS applications that are on the public internet anyway. If all your systems are cloud-based, a VPN may add little. Identity controls, device compliance, and endpoint protection deliver far more risk reduction. Keep a VPN for reaching internal systems that are not published to the internet.
4. Should small businesses require MFA for all employees?
Yes, without exemptions. Exempted accounts become the entry point, and the exemptions are almost always for executives or administrators, meaning the most valuable accounts. Use phishing-resistant methods such as passkeys or hardware security keys for administrators and anyone who can move money. Ensure everyone registers at least two methods so a lost phone does not lock someone out, and define a secure reset procedure that verifies identity properly.
5. How should businesses secure employee-owned devices?
Rather than trying to control the whole device, enforce a minimum standard as a condition of access: supported operating system, current security updates, disk encryption enabled, screen lock configured, and no jailbreaking. Use conditional access so non-compliant devices simply cannot reach company data. Keep company data inside managed applications with a separate work profile where the platform supports it, so you can remove company data without wiping personal photos. For anyone handling sensitive data, issue company-owned hardware instead.
6. Is antivirus enough for remote workers?
No. Traditional antivirus matches known malicious files, and most compromises today involve stolen credentials, phishing, or legitimate tools misused rather than files it would recognize. Antivirus is a baseline, not a strategy. Layer it with MFA, patching, email security, least privilege, and, as you grow, endpoint detection and response, ideally managed if nobody internally will watch the alerts.
7. How can small businesses protect cloud applications?
Configuration is your responsibility, not the provider's. Enforce MFA on all accounts including admins, limit the number of administrators and separate their admin accounts from daily use, restrict external sharing defaults, require admin approval for third-party app integrations, block legacy authentication protocols, enable audit logging with adequate retention, and configure alerts for suspicious sign-ins and new inbox rules. CISA's SCuBA baselines give you concrete settings for Microsoft 365 and Google Workspace.
8. What should an employee do after clicking a phishing link?
Report it immediately, ideally within minutes, and say exactly what happened including whether credentials were entered. Do not attempt to fix it quietly. The company should then disable the account, revoke all active sessions and refresh tokens (not just reset the password), re-register MFA, check for new inbox rules and forwarding, review recent file and mailbox access, and audit OAuth grants. Speed is everything: a report in five minutes is usually containable; a report in three days usually is not.
9. How often should remote employee access be reviewed?
Formal reviews quarterly, with immediate action on every joiner, mover, and leaver. Departures should be handled the same day, starting with disabling the identity provider account, which closes every SSO-connected application at once. Contractor and vendor access should carry expiry dates set at creation, so revocation happens by default. Quarterly reviews exist to catch what the day-to-day process missed, and they reliably find something.
10. What cybersecurity policies should a small business have?
Five short documents cover most needs: acceptable use, remote device and BYOD, data handling and classification, access control including onboarding and offboarding, and incident response. Add an AI usage policy, which is now essential. Keep each to two or three pages in plain language. A policy nobody reads provides no protection; a two-page document people actually follow provides quite a lot.
11. How can small businesses protect customer data with a remote team?
Know where it lives and minimize how many places that is. Classify it, restrict access to named people who need it, block or control external sharing, encrypt devices that touch it, keep it inside approved systems rather than local exports, define retention periods and delete what you no longer need, and back it up with a tested restore. Add contractual protection with any vendor that processes it, and be explicit with employees that customer data must never be pasted into unapproved tools, including AI assistants.
12. Should small businesses use an MSP or MSSP?
It depends on what you need. An MSP handles general IT: devices, help desk, patching, and basic security hygiene. An MSSP or MDR provider specializes in monitoring, detection, and response. Most businesses under about 50 people are best served by an MSP for IT operations plus a managed detection service if their data or risk justifies it. Ask any provider to state in writing which controls they own versus which remain yours, and whether they will actually respond to incidents or only notify you.
13. How often should cybersecurity training be provided?
Short, frequent training beats an annual session. Aim for something brief every month or two, plus immediate sharing of real phishing attempts as they arrive, plus a longer onboarding session for new starters. Run phishing simulations two to four times a year, measured as a program metric rather than an individual test. The most important outcome is not perfect click rates; it is that people report quickly and without fear.
14. What should a small-business incident-response plan include?
Named contacts with phone numbers stored offline, a clear definition of who can authorize disabling accounts and isolating devices, first-response steps for the three or four most likely scenarios (compromised account, lost device, suspected malware, suspected data exposure), your provider and insurer escalation paths, your notification obligations and deadlines, and a short post-incident review process. One page per scenario. Rehearse it once a year with a tabletop exercise.
15. How can businesses safely use AI tools with remote employees?
Approve specific tools rather than banning AI outright, since bans push usage into personal accounts where you have no visibility. Provision business or enterprise accounts with training on your data disabled and minimal retention. Write a short, explicit list of data that must never be entered: customer personal data, credentials and API keys, employee records, contracts, financial results, and proprietary code outside approved tools. Require human review of AI output used in customer-facing or production contexts. Require admin approval before any AI tool is connected to your email, files, or calendar. And make reporting accidental disclosure blame-free, because the alternative is not finding out.
16. Do small businesses really need cyber insurance?
It depends on your exposure and your ability to absorb a loss. Insurance can cover incident response costs, legal fees, notification, business interruption, and sometimes extortion payments, which for a small business can be the difference between recovery and closure. Be aware that insurers now require evidence of specific controls, commonly MFA, EDR, tested backups, and email security, and that policies may not pay out if the declared controls were not actually in place. The application process itself is a useful gap assessment.
17. What is the fastest thing we can do this week to improve security?
Enforce MFA on your email and identity provider for every account, starting with administrators, and remove any exemptions. If that is already done, verify that a backup restore actually works by restoring something. Those two actions address the most common cause of small-business compromise and the most common cause of small-business catastrophe.
The Practical Takeaway
A secure remote workforce does not require unlimited spending or an enterprise security department. It requires the right priorities applied consistently: secure identities with strong authentication, devices you can see and verify, access limited to what each role genuinely needs, data protected wherever it travels, backups you have actually tested, employees who report problems without fear, and a written plan for the day something goes wrong.
Most small businesses that suffer serious incidents were not defeated by sophisticated attacks. They were defeated by an account without MFA, a contractor whose access was never revoked, a backup nobody had restored, or a payment approved without a phone call. Those are all fixable, and none of them require a large budget.
Here is the practical next step. Open a document and write down three things: every system that holds your company's data, every person who can access each one, and whether MFA is enforced on it. That list will take an afternoon and it will tell you more about your actual risk than any product demo.
Then start closing the gaps it reveals, beginning with identity. Everything else in this guide gets easier once that foundation is in place.
Useful references for going further: CISA's Cyber Guidance for Small Businesses, CISA Cyber Essentials, the NIST Cybersecurity Framework and NIST Small Business Cybersecurity Corner, FTC cybersecurity guidance for small business, CISA StopRansomware, the Verizon Data Breach Investigations Report, and the FIDO Alliance on passkeys.